CrowdEye
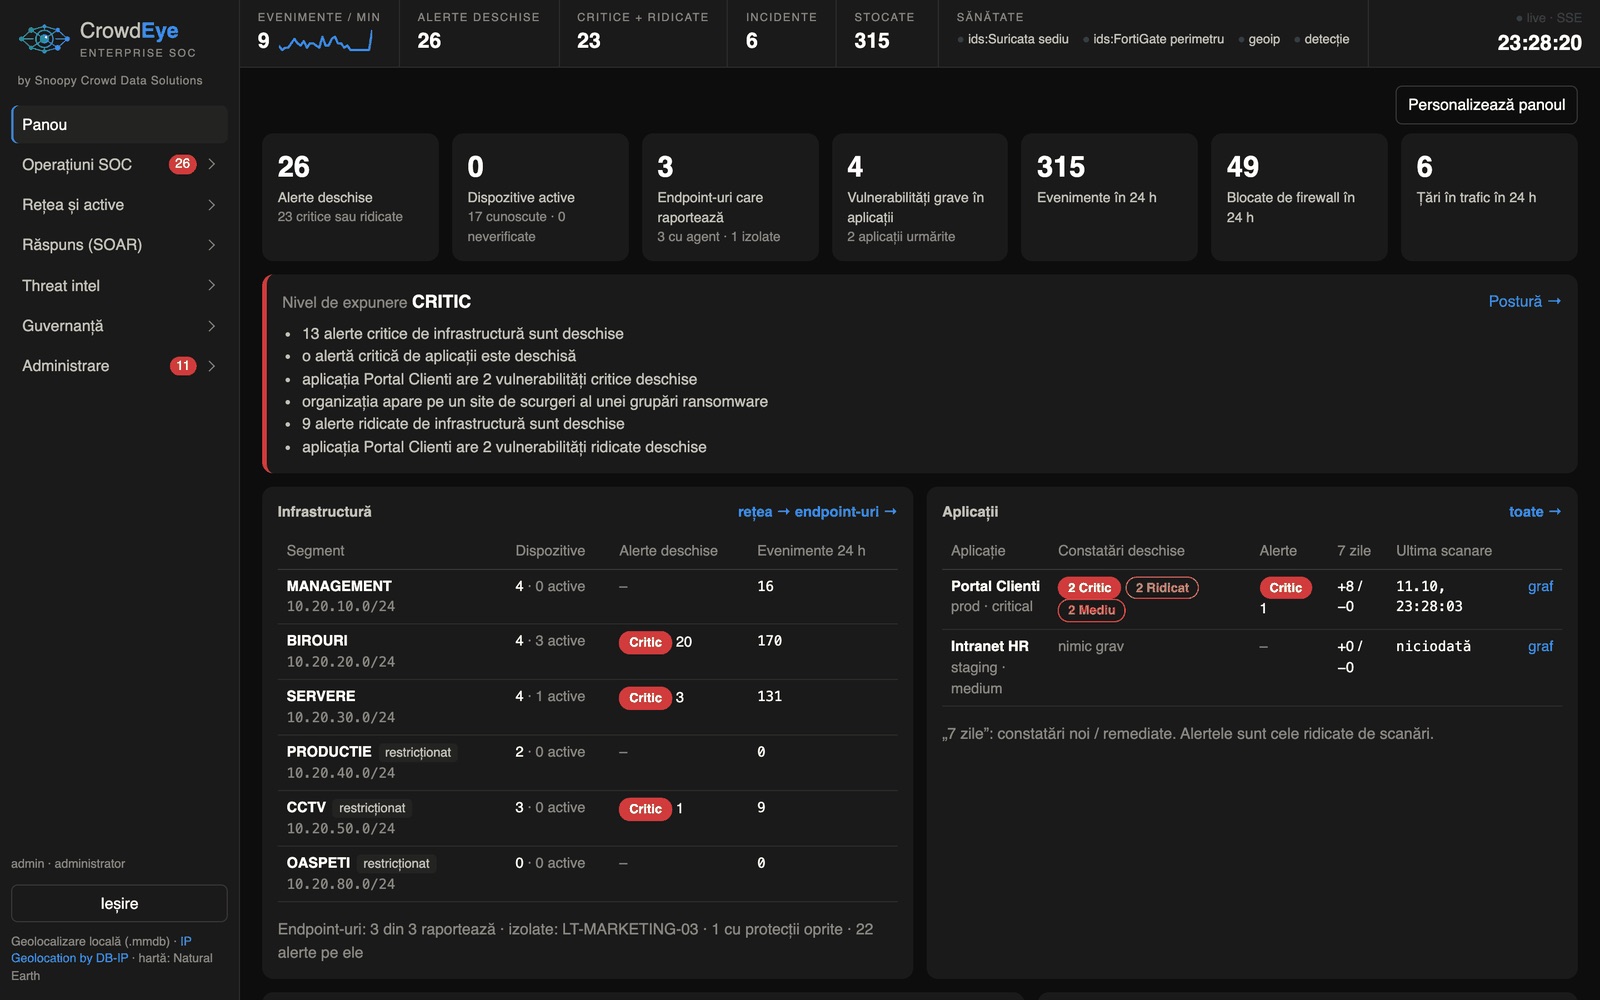
The security operations centre that stays inside the client's infrastructure. Network detection, EDR, IDS, application security, automated response and NIS2 and DORA reporting — a single on-premise platform.
NIS2 and DORA reporting from the case file
Assisted classification against the legal criteria and a deadline clock: 24 h, 72 h and one month for NIS2, 4 h for DORA. The report to the authority is built from the incident case file.
Explained detection
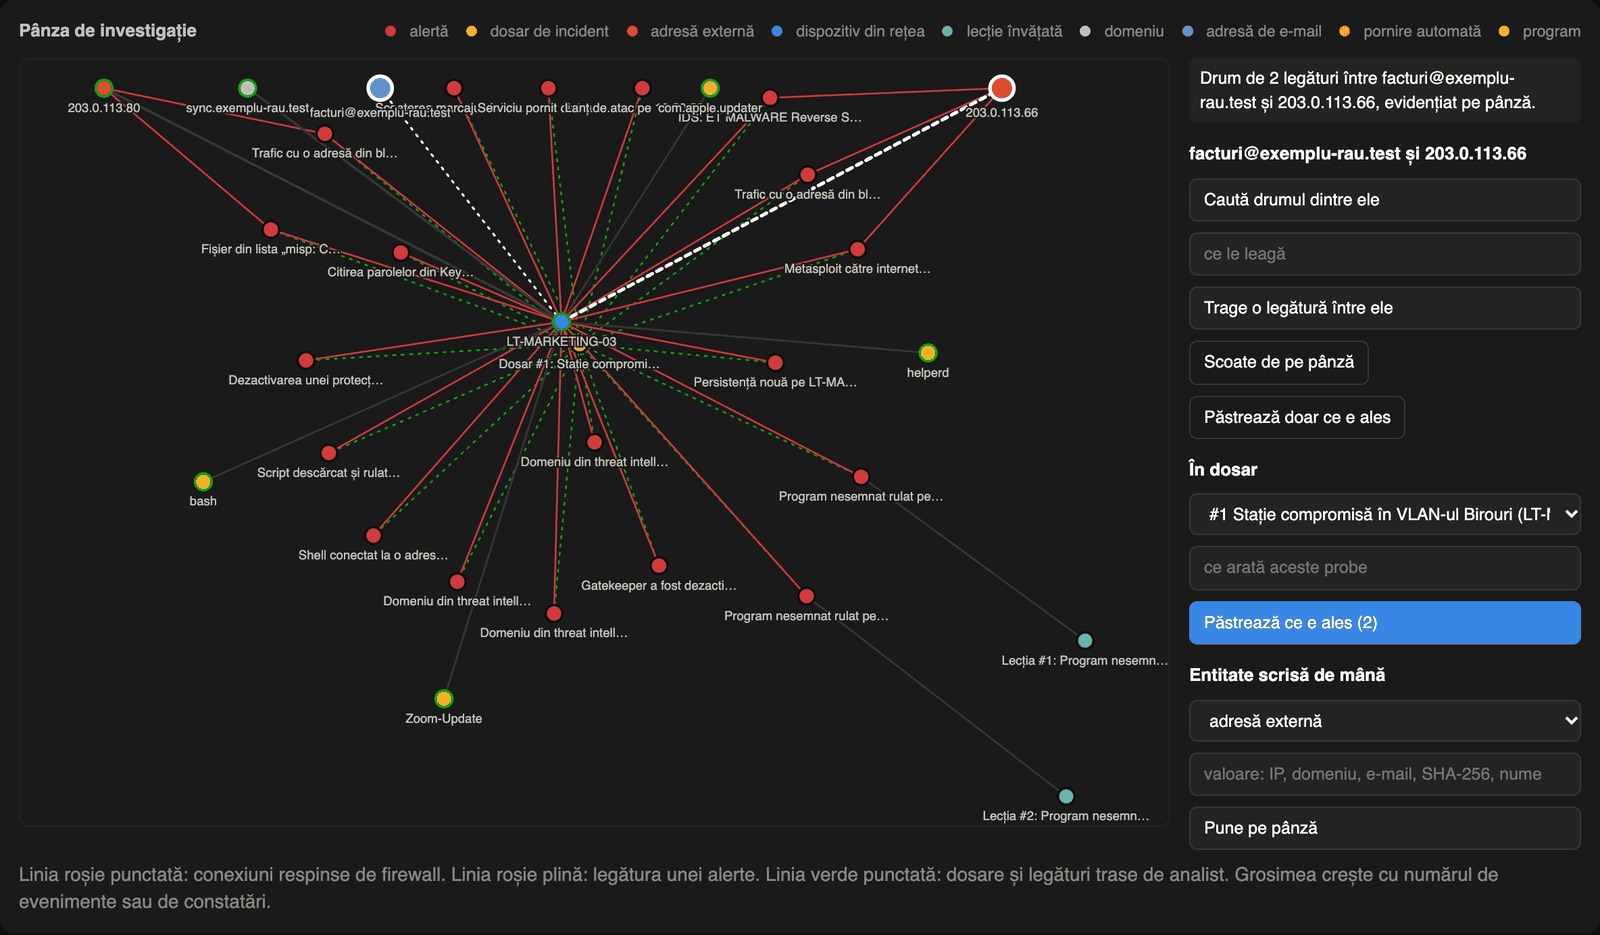
Active rules, alerts correlated into incidents, with evidence events and the MITRE ATT&CK technique. Coverage is measured from the data that actually arrives, not declared.
EDR for workstations and servers
Windows, macOS, Linux and FreeBSD. Isolation, blocking, quarantine and evidence collection, with four-eyes approval. Signed agent, no arbitrary commands.
IDS, threat intelligence and AppSec
Suricata and Snort sensors, indicators from MISP, OTX and TAXII 2.1, CVEs with NVD scores. Code, dependency, IaC, API and DAST testing.
Automated response (SOAR)
Predefined playbooks, disabled at install, connectors and protected targets that no automated step can touch.
Local AI, humans decide
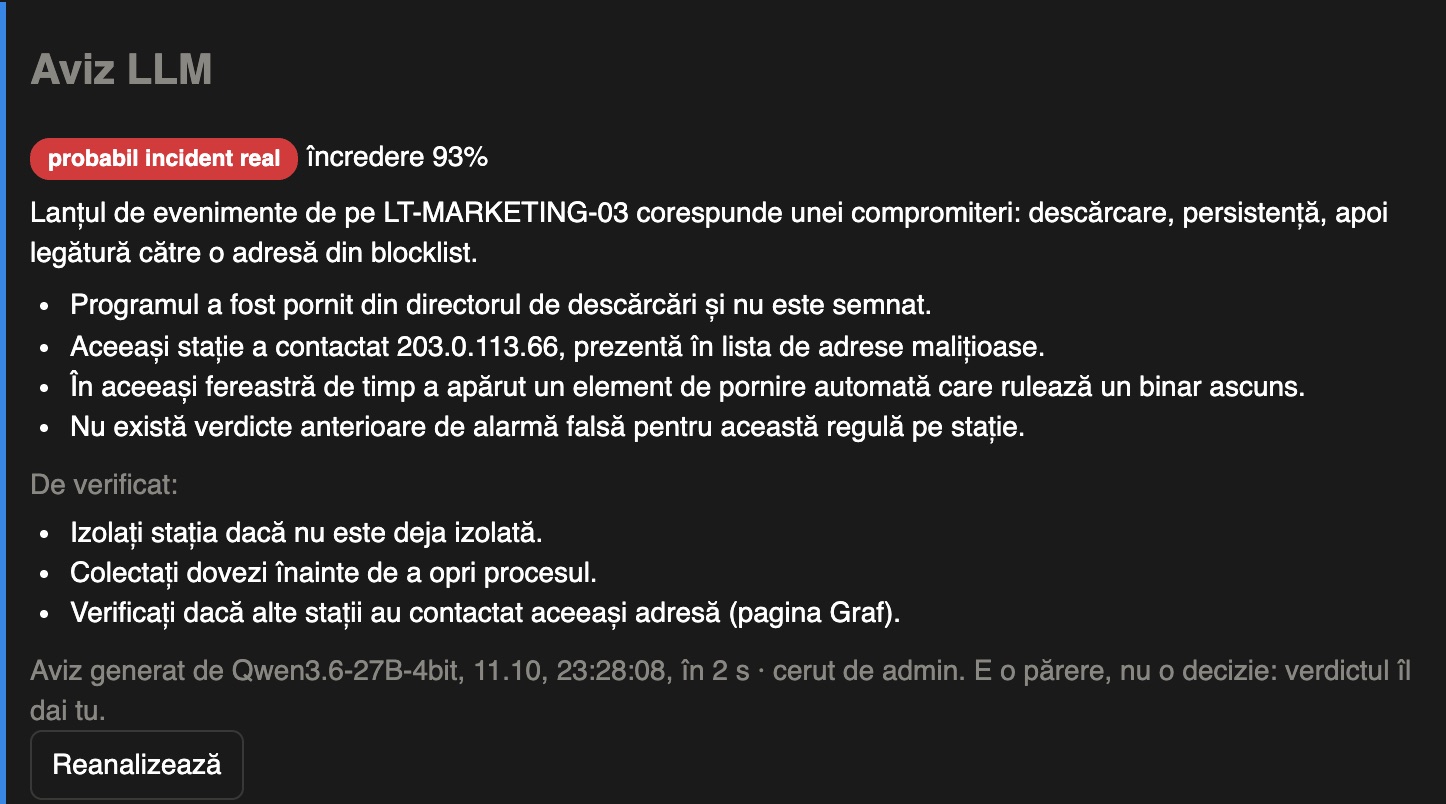
Verdicts on alerts and the incident narrative, from a model running at the client. The AI never closes alerts or executes anything on its own.